Firewall Rule Audit: Find the Dead Rules
Find unused firewall rules on a Linux box with nftables counters, then retire them safely with a snapshot-and-diff routine, a jq script, and a systemd timer.
All the articles with the tag "networking".
Find unused firewall rules on a Linux box with nftables counters, then retire them safely with a snapshot-and-diff routine, a jq script, and a systemd timer.
Put smart plugs and TVs on an IoT VLAN, then fix Chromecast, AirPlay and Sonos discovery with an mDNS reflector and the right firewall rules. Configs included.
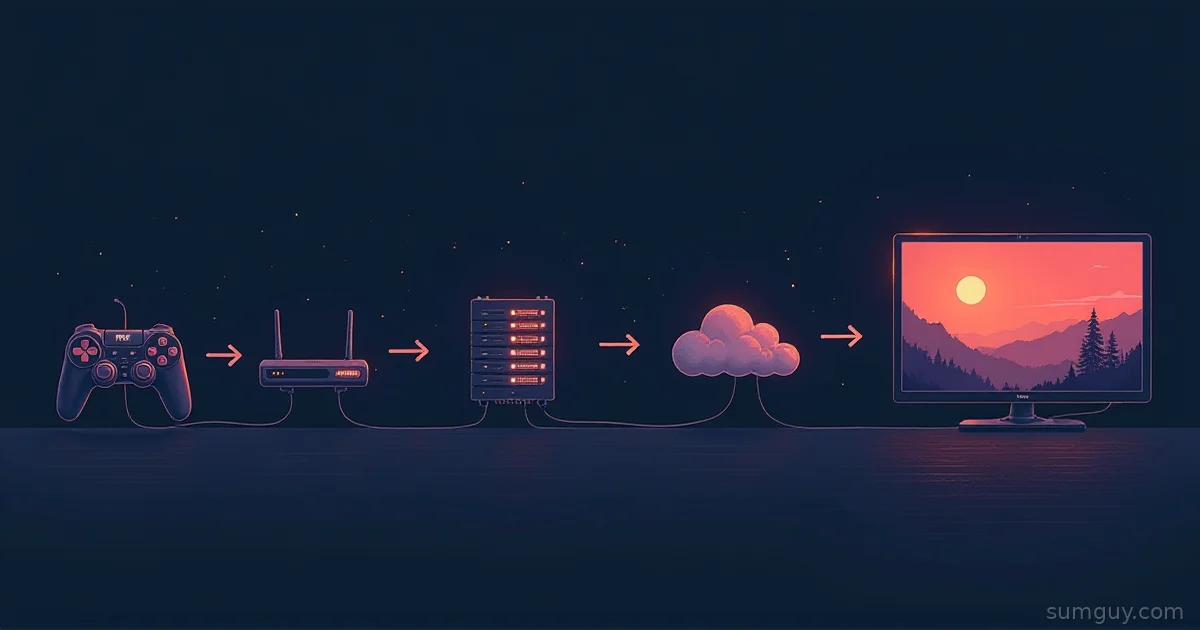
Ping is one stage of seven in a game stream's latency chain. Learn what else adds milliseconds, how to measure each stage, and which fixes pay off first.
Make jellyfin.home.example.com resolve to a LAN IP at home and over WireGuard or Tailscale, and to your public IP elsewhere. Unbound and AdGuard Home configs.
Mass scanners find a new home lab IP within hours. Audit what the internet can reach, from UPnP to Docker ports to IPv6, then build a threat model that fits.
Self-hosted is not silent. Audit outbound calls with DNS query logs, watch live connections, block egress with Docker networks, then flip telemetry opt-outs.
Rebuild Docker's bridge network with ip netns, veth pairs, a Linux bridge and nftables NAT. Six iproute2 commands, three nft rules, and a 2 AM debugging edge.
VLAN configured but traffic still breaks? Native VLAN mismatches, PVID traps on cheap switches, Proxmox bridge gotchas, and Docker macvlan fixes, with commands.
Configure OPNsense gateway groups for WAN failover and load balancing, then layer policy-based routing so specific hosts or VLANs use a chosen WAN link.
One central CrowdSec LAPI, remote log-parsing agents, and bouncers on every box, so an SSH brute-force on one server gets blocked everywhere else too.
NetAlertX v26.9.0 ships a built-in MCP server with 12 tools. Learn how to wire it into Claude Code, what it exposes, and when to use Home Assistant instead.
Dual-stack IPv6 for home labs: DHCPv6-PD delegation, stable addressing past SLAAC privacy extensions, real nftables firewall rules, and Docker IPv6 done right.